Vulnerability detail retention policy
To ensure long-term performance and manage database size, Invicti is introducing a Vulnerability Detail Retention Policy. Starting 1 September 2025, HTTP request and response data for vulnerabilities older than 6 months is automatically removed from all supported cloud environments.
This change optimizes infrastructure to improve overall system performance while maintaining visibility.
What changed on 1 September 2025
The content of the HTTP Request/Response tab is removed from the Scan Summary page for vulnerabilities older than 6 months.
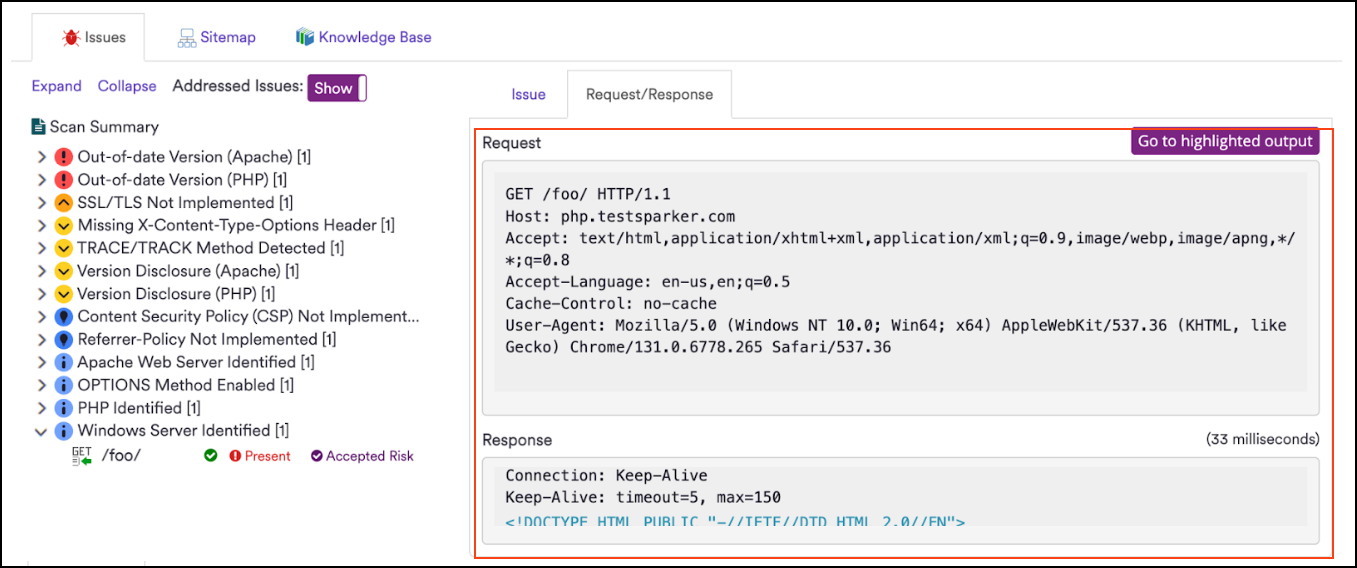
- No vulnerabilities or scans are deleted—only the HTTP request/response data is removed.
- HTML/PDF reports such as the Detailed Scan Report are also impacted.
- The vulnerability record itself remains available.
- In place of the removed data, you see this notice: The HTTP request/response data for this vulnerability is no longer available because it's older than 6 months. To view this information, view a more recent vulnerability or run a new scan for this target.
Example behaviour
If a target is scanned weekly for a year and the same vulnerability (for example, "Windows Server Identified") appears in every scan:
- The system retains the latest instance of that vulnerability for the target.
- Older instances lose HTTP request/response details, but not the overall record or scan metadata.
Affected environments
This policy applies to all multi-tenant cloud environments:
- United States
- US2
- EU
- CA
When this takes effect
- Initial cleanup: On 1 September 2025, Invicti performs a one-time batch update to remove HTTP request and response details from vulnerabilities older than 6 months.
- Ongoing policy: A rolling 6-month window is applied moving forward.
What you should do
No action is required. This change is applied automatically in applicable environments.
If you wish to preserve older vulnerability details:
- Consider exporting relevant data, such as downloading a Detail scan report, before 1 September 2025.
- Schedule a new scan to refresh vulnerability results with full details.
FAQ
Does this impact vulnerability status or reporting?
No. Vulnerability status (for example, active, fixed, false positive) and scan metadata remain unaffected.
Can I turn this policy off in the cloud?
No. This retention policy is applied automatically to all supported cloud environments.
If you have any questions or need help exporting vulnerability data, contact the support team.
Need help?
Invicti Support team is ready to provide you with technical help. Go to Help Center