Deployment: Invicti Platform on-demand
CyberArk Vault integration
Connect Invicti Platform to CyberArk so that Invicti Platform retrieves scan credentials directly from your vault when authenticating scans. The integration syncs secrets one-way, so credentials remain in CyberArk as the single source of truth - Invicti Platform stores only a reference to each secret, never the value itself.
This document explains how to configure the CyberArk Vault integration for CyberArk Enterprise Password Vault (EPV), and how to add vault-sourced secrets for use in scans.
Why this matters
When scan credentials are stored directly in Invicti Platform, rotation requires updating every target configuration individually. By connecting Invicti Platform to CyberArk, credential management stays consolidated in your vault. Invicti Platform resolves each secret at scan time, so it always uses the current value - no manual updates needed when passwords rotate.
Before you begin
Have these details ready before you start:
- The URL of your Central Credential Provider (CCP), up to the port number. Don't add a path - Invicti Platform appends
/AIMWebService/api/Accountsautomatically. - The Application ID that Invicti Platform uses to request credentials. You must register the application in CyberArk and give it permission to retrieve accounts from the Safe.
- The name of the Safe that holds your credentials.
- A client certificate in
.pfxformat that authenticates Invicti Platform to CyberArk, and its password if the certificate is password-protected. Export the certificate with AES-256 (PBES2) encryption. Certificates that use legacy encryption such as RC2 aren't supported by default.
The accounts that hold your scan credentials must already exist in CyberArk before you can reference them in Invicti Platform. Refer to the CyberArk documentation for instructions on creating accounts and Safes.
The CyberArk URL you enter must be accessible from Invicti Platform's cloud infrastructure. Scans can't retrieve credentials from a vault that's unreachable at scan time. If your vault is behind a firewall, add Invicti Platform's IP addresses to your allowlist. Refer to the Trustlist requirements documents for the addresses for your region.
Configure the CyberArk Vault integration
- Select Integrations from the left-side menu.
- Find the CyberArk Vault card and click Configure.
- Enter an Integration name to identify this connection in Invicti Platform.
- If you want all users in your organization to be able to select this integration when creating a secret, enable the Visible to everyone toggle. When enabled, other users can select the integration in the secret picker but can't edit or delete it - only you and users with the Integrations permission can manage the connection.
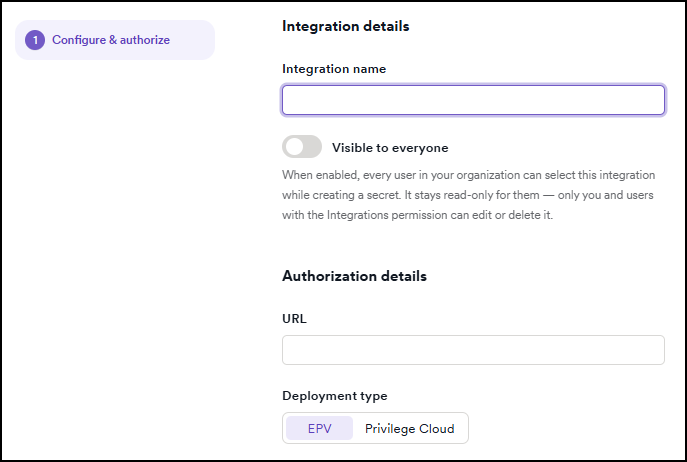
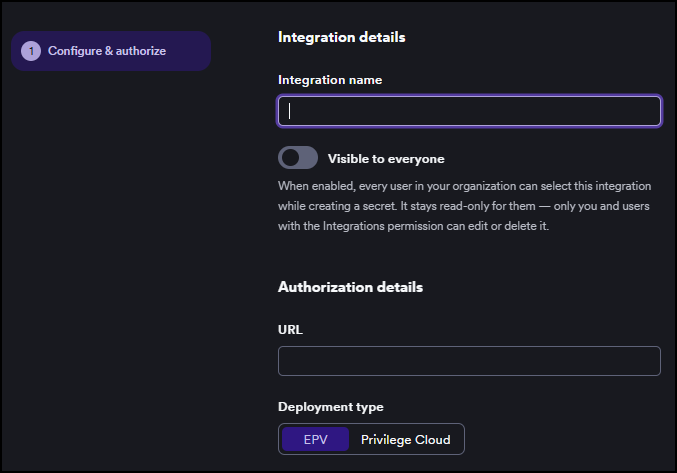
- Under Authorization details, enter the URL of your Central Credential Provider (CCP) up to the port number. Don't add a path - Invicti Platform appends
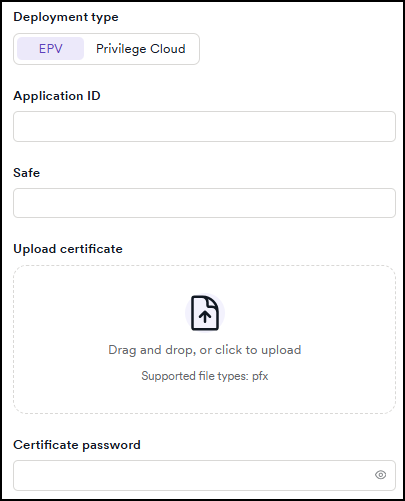
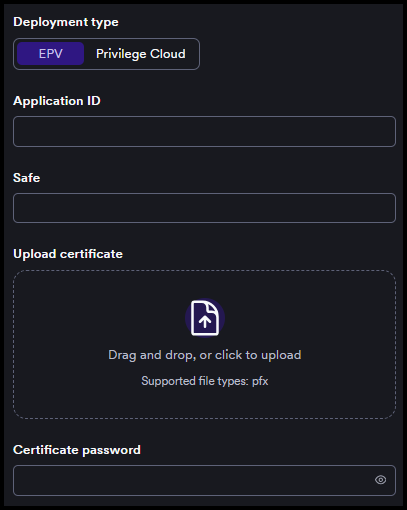
/AIMWebService/api/Accountsautomatically. - Select EPV as the Deployment type.
- Complete these fields:
- Application ID - the application ID registered in CyberArk for Invicti Platform.
- Safe - the name of the Safe that holds your credentials.
- Upload certificate - drag and drop your
.pfxclient certificate, or click the area to select the file. - Certificate password - the password of the certificate. Leave it empty if the certificate isn't password-protected.
- Click Validate and save.
Invicti Platform checks that all required fields are filled in and sends a request to the Central Credential Provider with your certificate and Application ID. If the connection fails, Invicti Platform shows an error and doesn't save the integration. If it succeeds, Invicti Platform saves the configuration and the integration appears on the Integrations page.
To check at any time that a saved integration still works, open the integration in edit mode and click Test connection. You don't need to change anything. Validate and save checks new changes before it saves them, while Test connection checks the settings you last saved, so save any changes first. A message appears confirming that the connection was verified, or describing what failed. The message never shows your credential values.
On success, the message is "Connection verified successfully." If the vault can't be reached and no specific reason is available, the message is "Could not connect to the vault. Check your configuration and try again."
Update the integration
To change a saved integration, select Integrations from the left-side menu and open the CyberArk Vault integration.
Invicti Platform never shows the saved certificate or certificate password. Keep this in mind when you edit:
- If you change only the Integration name or the Visible to everyone toggle, you don't need to enter the certificate again.
- If you change the URL, Application ID, Safe, or Deployment type, you must enter the certificate again before you can save.
Add a vault-sourced secret
Once the integration is configured, you can add secrets that Invicti Platform retrieves from your vault. Vault-sourced secrets work the same way as secrets stored in Invicti Platform - you reference them by name in any credential field. CyberArk secrets work for scans that run on cloud agents and on internal agents.
- Open a target's authentication settings by selecting Inventory > Targets from the left-side menu, then opening the target and clicking Edit.
- Select an authentication method - for example, Simple form - to display the credential fields.
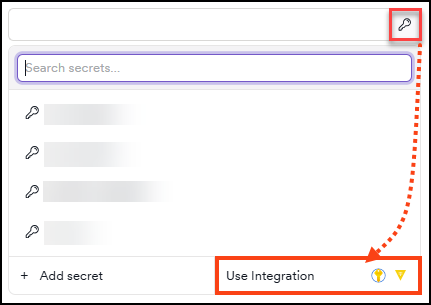
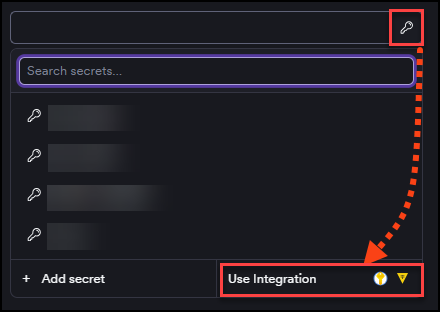
- In a credential field (for example, Username or Password), click the key icon to open the secret picker.
- Click Use integration at the bottom of the picker.
- In the Use integration dialog, complete the fields:
- Integration name - the vault connection to use. If you have only one connection configured, this field is pre-selected.
- Name - a name for this secret in Invicti Platform. Use something descriptive, for example
prod_db_password. - Folder - the CyberArk folder inside the Safe that holds the account, for example
Root. To reference a subfolder, separate the folder names with a backslash, for exampleRoot\Subfolder. Don't use a forward slash. - Object - the name of the account object in CyberArk, for example
testobject. - Secret availability - who can use this secret:
- Only me - only you.
- Entire org - all users in your organization.
- Specific teams - users in selected teams only.
- Specific users - selected users only.
- Click Test vault settings to verify that Invicti Platform can retrieve this specific secret from the vault. If it can, the message is "Vault settings verified successfully."
- Click Save. The credential field shows the secret name in
{{secretName}}format. - Save the target configuration. The secret is now active for scans on this target.
The secret also appears on the Scans > Secrets page with Source listed as Vault integration.
The Audit log records when you create, update, or delete secrets. If you have the required permissions, select Audit log from the left-side menu to review these entries.
To use vault-sourced secrets in other authentication methods such as LSR, refer to Using secrets in scans. For full details on secret availability options and how secrets work across scan configurations, refer to the Secrets document.
Troubleshooting
Validate and save is unavailable
The button stays disabled until all required fields are filled in. This includes Application ID, Safe, and the certificate. The URL must be a valid URL.
When you edit a saved integration and change the connection settings, you must also enter the certificate again.
Validate and save fails for EPV
If Invicti Platform can't connect to CyberArk or retrieve from your Safe, it shows the message that CyberArk or the connection returned. Common messages and what to check:
-
Wrong Safe
CyberArk returned status 404 Not Found. APPAP004E: Password object matching query [Safe=wrongsafe] was not found (Diagnostic Info: 1). Please check that there is a password object that answers your query in the Vault and that both the Provider and the application user have the appropriate permissions needed in order to use the password.
In the message, the name after
Safe=is the value you entered in the Safe field. Check that the Safe name is correct, and that the application has permission to retrieve accounts from it. -
Wrong Application ID
CyberArk returned status 400 Bad Request. APPAP423E: An error occured while trying to connect to the vault with webservice app: wrongappid. Error code: 9.
The name after
webservice app:is the value you entered in the Application ID field. Check that the application is registered in CyberArk with exactly this ID. -
Wrong host in the URL
Connection failed: Name or service not known (wronghost.example.com:9797)
The host name and port in brackets are the ones from the URL field. Check the host name and the port, and that the address is reachable from Invicti Platform's cloud infrastructure.
Test connection fails
Check that the CyberArk URL is reachable from Invicti Platform's cloud infrastructure. A vault accessible only within your internal network doesn't work.
If the URL is reachable, verify the following:
- The Application ID and Safe are correct.
- The application has permission to retrieve accounts from the Safe.
- The certificate password is correct.
If the certificate has expired or been rotated in CyberArk, open the integration in edit mode, upload the new certificate, and click Validate and save. Then click Test connection to confirm the connection works.
The client certificate (.pfx file) you uploaded can't be loaded
This applies to the .pfx file you upload in the Upload certificate field. If Invicti Platform can't read it, it shows this message:
Unable to load the client certificate. Verify the certificate password is correct and the file is not corrupted. If both are correct, the certificate may use a legacy encryption algorithm (e.g. RC2) that is no longer supported by default — try re-exporting it using AES-256 (PBES2) encryption.
The same message appears for a wrong password, a corrupt file, and an unsupported encryption algorithm. Check the following in order:
- Invalid file type - the upload accepts
.pfxfiles only. - Wrong password - enter the password you set when you exported the certificate. Leave the Certificate password field empty if the certificate isn't password-protected.
- Corrupt file - export the certificate again and upload the new file.
- Legacy encryption - Invicti Platform doesn't support certificates encrypted with legacy algorithms such as RC2 by default. Re-export the certificate using AES-256 (PBES2) encryption, then upload the new file.
The connection fails because of the CyberArk server's own certificate (host name mismatch)
This isn't about the .pfx file you upload. It concerns the HTTPS certificate that your CyberArk server presents when Invicti Platform connects to it. Invicti Platform rejects the connection if that certificate was issued for a different host than the one in the URL field. Make sure the URL uses the host name that the server's certificate was issued for.
Test vault settings fails in the Use integration dialog
Test vault settings checks whether Invicti Platform can retrieve the specific secret you entered, not only whether the vault is reachable. If the vault doesn't respond, the message is "Connection timed out". Check that the CyberArk server is running and reachable from Invicti Platform's cloud infrastructure.
If the vault responds but the secret can't be retrieved, check the secret details. Confirm that the Folder and Object values match what's configured in CyberArk exactly, including case. Separate nested folders with a backslash (Root\Subfolder), not a forward slash. Also check that the secret is in the Safe configured on the integration.
The integration can't be deleted
The integration can't be deleted while active secrets still reference it. Open Scans > Secrets and remove or reassign any secrets that use this integration, then try deleting the integration again.
The Use integration button doesn't appear in the secret picker
The Use integration button appears only when you have at least one secret manager integration configured. Confirm you saved the CyberArk Vault integration successfully under Integrations. If it was deleted or failed to save, configure it again following the steps in this document.
Need help?
Invicti Support team is ready to provide you with technical help. Go to Help Center