Vulnerabilities overview
This document explains the information found on the Vulnerabilities page.
Information available on the Vulnerabilities page
This section describes each of the available fields you can view on the vulnerabilities page. There are two types of view: by Type and by Vulnerability. Use the former to group all vulnerabilities by type, across all the target scans. Use the latter to see individually all vulnerabilities, across all the target scans. By clicking the Columns button, you can adjust the visibility of information.
From either view, you can open a vulnerability to see its details, including CWE ID, CVSS v3.0, and CVSS v4.0 scores. For more information, refer to the View vulnerability details document.
View by Type
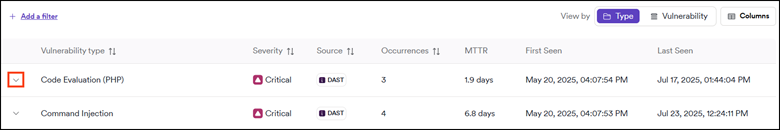
To customize the page view, click Columns and select the information you want to see.
Vulnerability type
Shows the type of the vulnerability found. Click the arrow by the vulnerability type name to show all occurrences of the vulnerability across all scans and further details: file/URL, target, source, status, confidence, last seen, first seen, assignee, and tags. For more information regarding the details, refer to the View by Vulnerability section.
Severity
Shows the severity level of the found vulnerability: critical, high, medium, low, or informational.
Source
Displays how the vulnerability was identified - either through DAST, SAST, SCA, or Container Security scan results.
Occurrences
Displays the number of occurrences of each vulnerability across all scans.
MTTR
Mean time to remediate the vulnerability type.
First seen
Lists the first date and time in which Invicti identified the vulnerability.
Last seen
Lists the last date and time in which Invicti identified the vulnerability.
View by Vulnerability
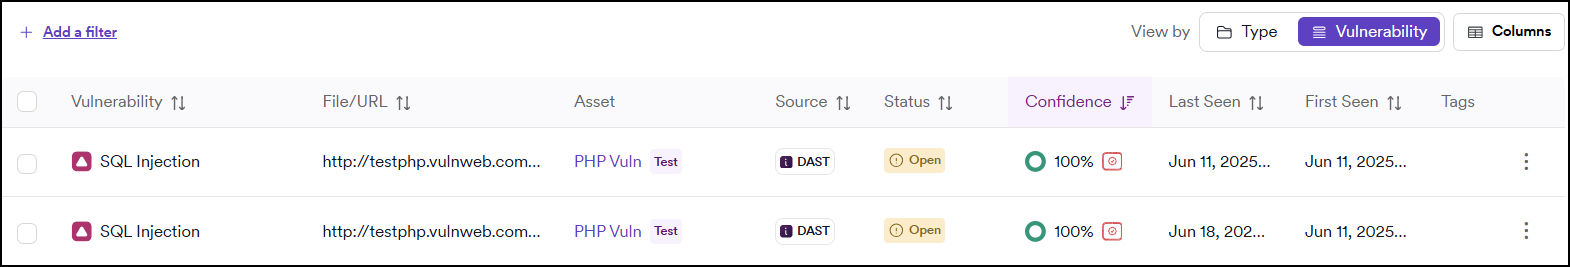
To customize the page view, click Columns and select the information you want to see.
Vulnerability
The name of each vulnerability identified by Invicti Platform with icon showing severity level: critical, high, medium, low, or informational.
File/URL
The file or URL where the vulnerability was identified.
Vulnerability ID
Displays the vulnerability ID. The column isn't visible by default.
Asset
Name of the target and environment type where the vulnerability was identified.
Source
Displays how the vulnerability was identified - either through DAST, SAST, SCA, or Container Security scan results.
Status
The status of the vulnerability can be: Open or Rediscovered, Fixed (Unconfirmed) or Fixed, Ignored, or False Positive.
You can't manually change the Rediscovered and Fixed statuses. Invicti updates these automatically based on retest or scan results. For more information, refer to the Retest vulnerabilities document. To retest all vulnerabilities found by a scan at once, refer to Retest all vulnerabilities found by a scan.
Confidence
Lists the confidence level, showing how certain Invicti Platform or SAST integration is of the vulnerability it identified.
First seen
Lists the first date and time in which Invicti identified the vulnerability. The column isn't visible by default.
Last seen
Lists the last date and time in which Invicti identified the vulnerability.
Assignee
This displays the user name of the person to whom the vulnerability is assigned. The column isn't visible by default.
Tags
Lists the tags you assigned to the vulnerability. The column isn't visible by default.
Vulnerability actions
Actions available on the All vulnerabilities page for individual or bulk changes.
Vulnerability-specific actions:
- Export to a .csv, .json, or .xml format.
- Generate report
- Mark to change status
- Comment or add tags
- Retest
- Integrate with issue tracker
Export
Allows to export the information on all vulnerabilities to a file in .csv, .json, or .xml format.
Bulk actions
After enabling the checkbox by multiple vulnerabilities, click Bulk action to select an action:
- generate report,
- change of status of vulnerabilities,
- comment or add tags
- retest
- send the vulnerabilities to the issue tracker system (after the integration).
Filtering vulnerabilities
It’s possible to filter the vulnerabilities by applying one or more of the filters. Available filter options differ depending on the view selected:
- CWE or Common Weakness Enumeration.
- Threat severity: critical, high, medium, low, information.
- Source: DAST, SAST, SCA or Container Security scan.
- Occurrences: number of occurrences.
- Is on API: no or yes options.
- Application: indicates if the vulnerability is associated with a specific application.
- Asset: indicates if the vulnerability is associated with a specific asset.
- Collection: indicates if the vulnerability is associated with a specific collection.
- URL: the reference to the resource that contains the issue.
- Environment where the vulnerability was found: Not specified, Production, Pre-Production, Test, Development.
- Status of the vulnerability: Rediscovered, Open, Fixed, Fixed (Unconfirmed), False Positive, Ignored.
- Vulnerability: name of the vulnerability.
- Confidence: the certainty with which Invicti Platform or SAST integration identified the vulnerability.
- Assignee: person assigned to the vulnerability.
- Tags: tags assigned to the vulnerability.
- First seen: date when the vulnerability was first identified.
- Last seen: date when the vulnerability was last identified.
Need help?
Invicti Support team is ready to provide you with technical help. Go to Help Center